


Ship secure code
at agentic speed.
Remove entire classes of vulnerabilities before hitting commit, run deep detection, autotriage, and autofix workflows, and access the entire Semgrep platform via MCP.

Find and fix the issues that matter in your code (SAST)

Fix vulnerabilities in open source dependencies and block malware

Find and fix hardcoded secrets with semantic analysis

Scan and fix AI-generated code the moment it's written

Combine AI reasoning with rule-based analysis for detection, triage, and remediation

Automate, manage, and enforce security across your organization

Build and deploy security pipelines that combine static analysis with AI at scale

Protect against software supply chain attacks

Increase security while accelerating development

Prevent the most critical web application security risks

Protect Your Code with Secure Guardrails

Mitigate software supply chain risks
Increase security while accelerating development

Want to read all the docs? Start here

Get the latest news about Semgrep
See how Semgrep can save you time and money

Join the friendly Slack group to ask questions or share feedback
Join us at a Semgrep Event!
See why users love Semgrep
View our library of on-demand webinars
Ship secure code
at agentic speed.
Remove entire classes of vulnerabilities before hitting commit, run deep detection, autotriage, and autofix workflows, and access the entire Semgrep platform via MCP.
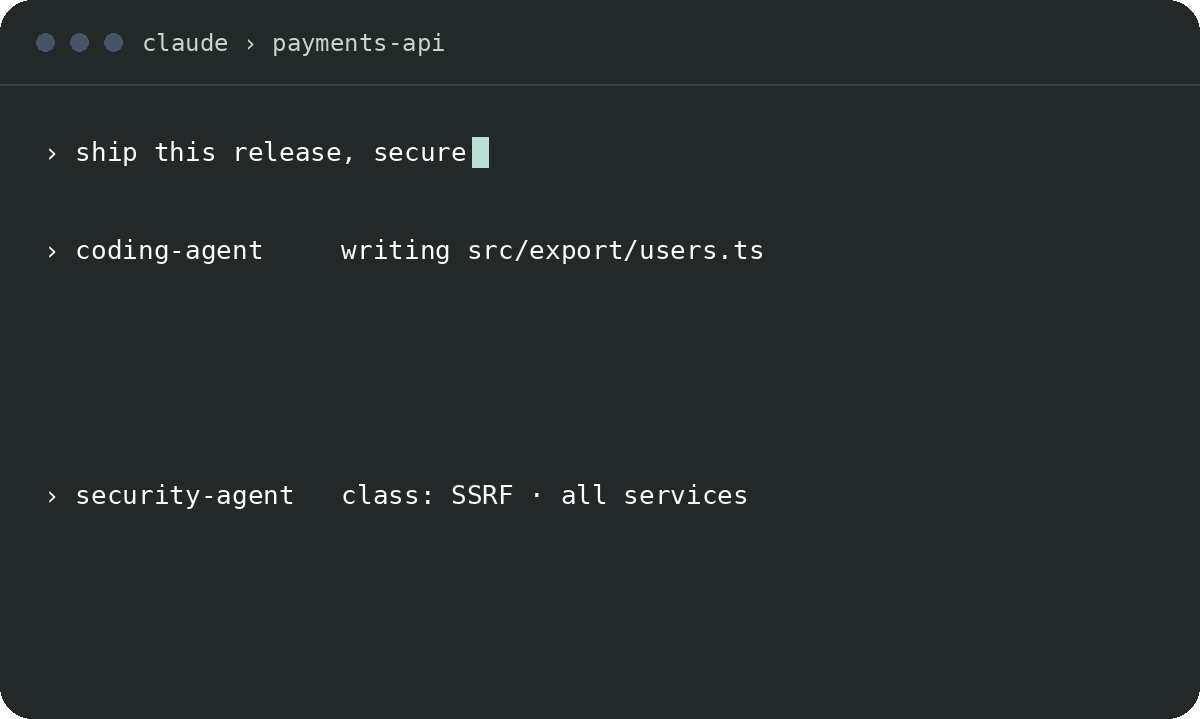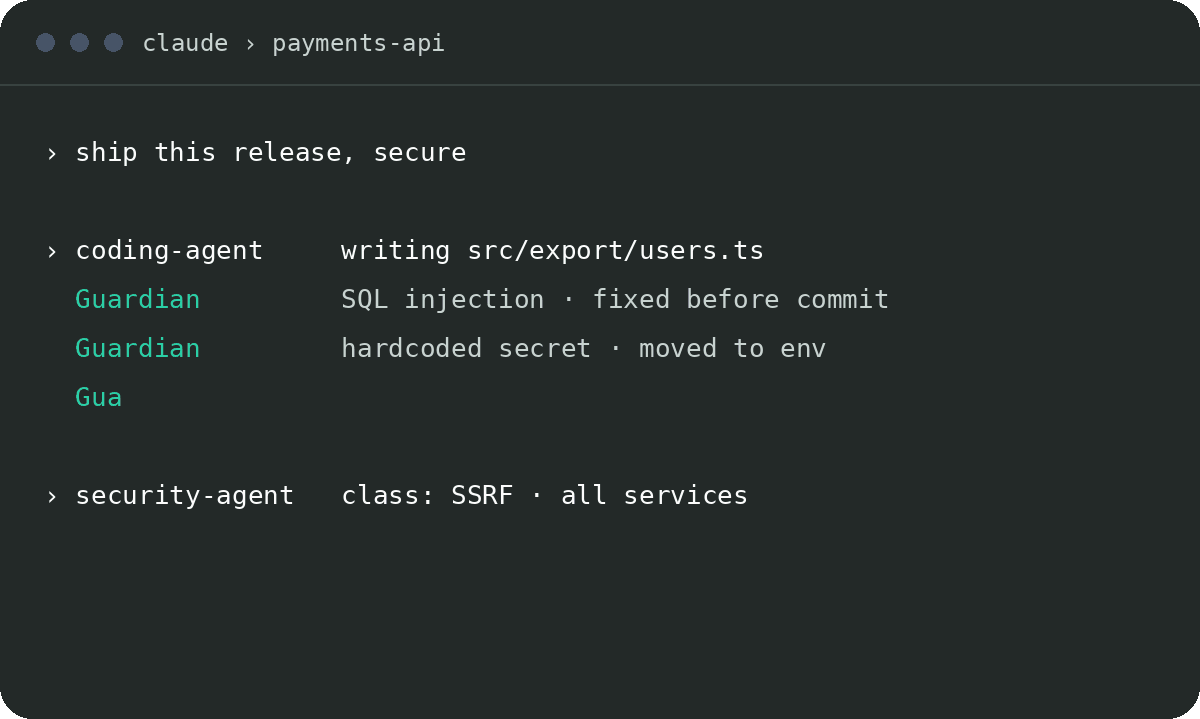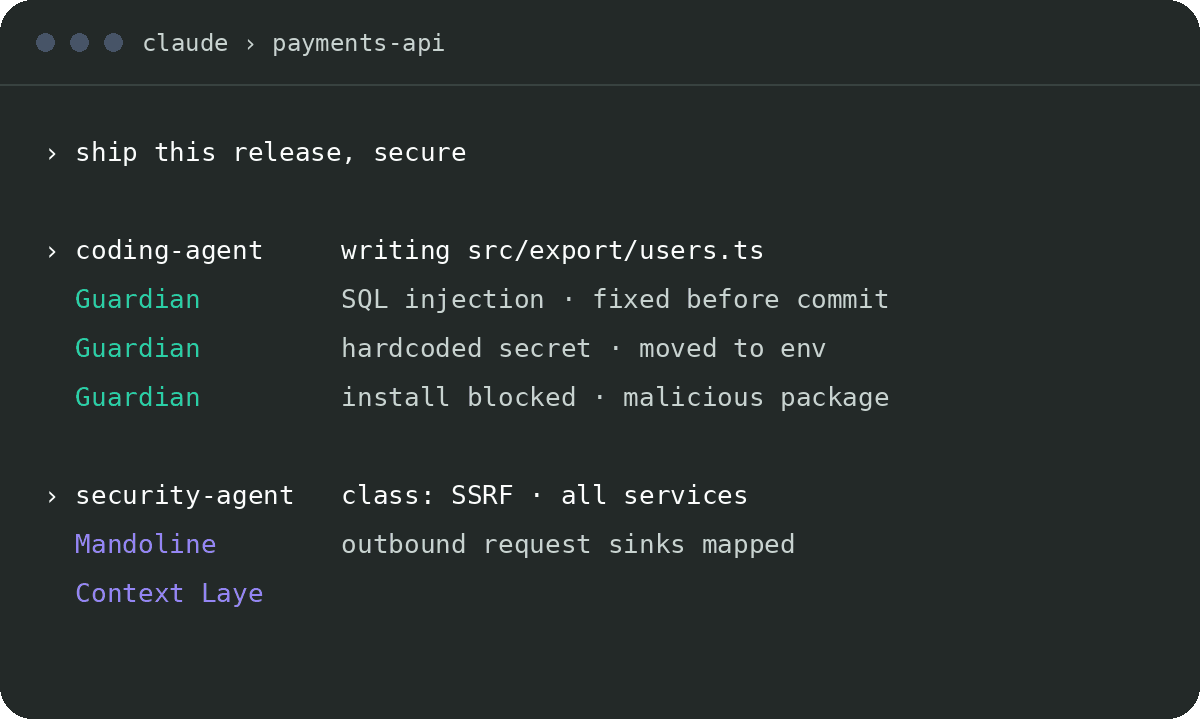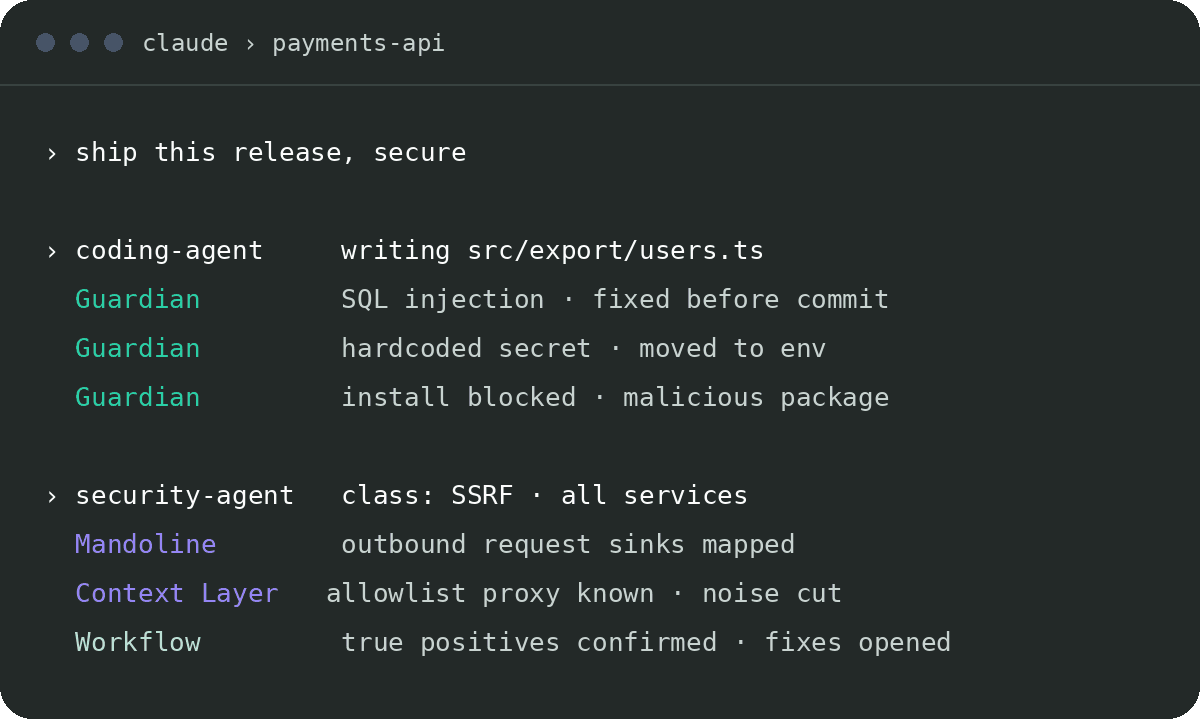
Remove the security bottleneck.
Give any agent the full Semgrep platform.
The Semgrep MCP server gives your agents the tools to act on whole vulnerability classes, not one vulnerability at a time. Just point your agent at the server.
Secure agent-written code at generation
Guardian works in any coding harness and catches risks before they reach a commit. Your agents are guided to secure, policy-compliant code, preventing additional PRs for your security team to review.
Semgrep's agents run complex detection on their own.
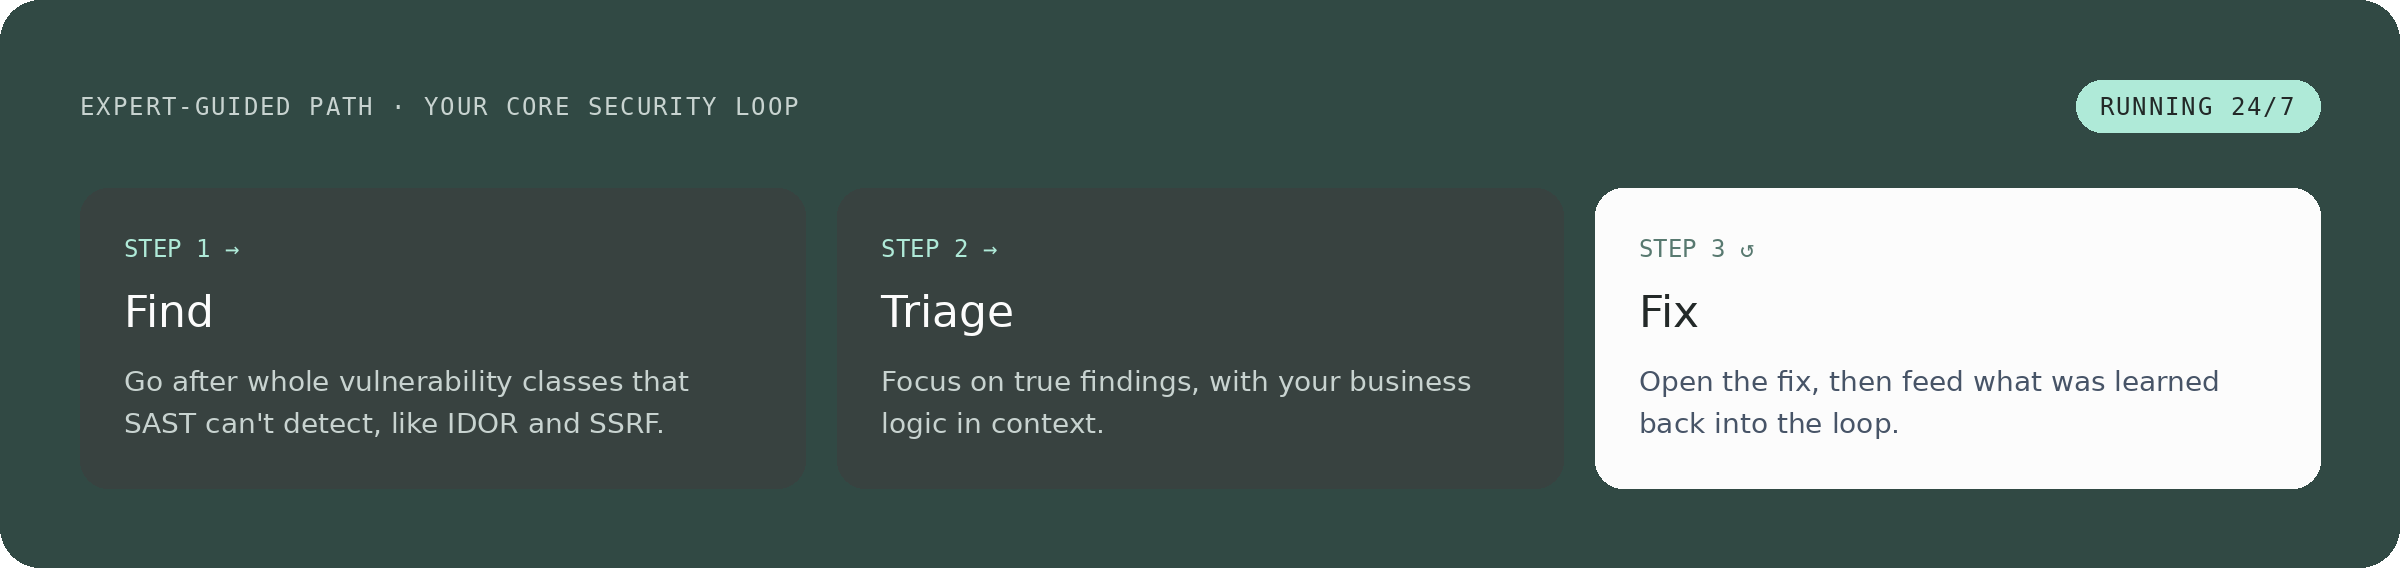
Agentic Security Workflows follow a guided path and best practices set by Semgrep's security experts. Chain detection, vulnerability hunting, triage, and fixes into a loop that runs around the clock, in Semgrep cloud or your CI.
Give your agents a head start by grounding them in facts.
Mandoline deterministically answers code-flow and reachability questions in milliseconds, so agents don't waste tokens or time grepping through repos.
Context layer provides persistent, complete, and correct answers across apps and repos, giving agents the guardrails they need to assess security impact at scale.
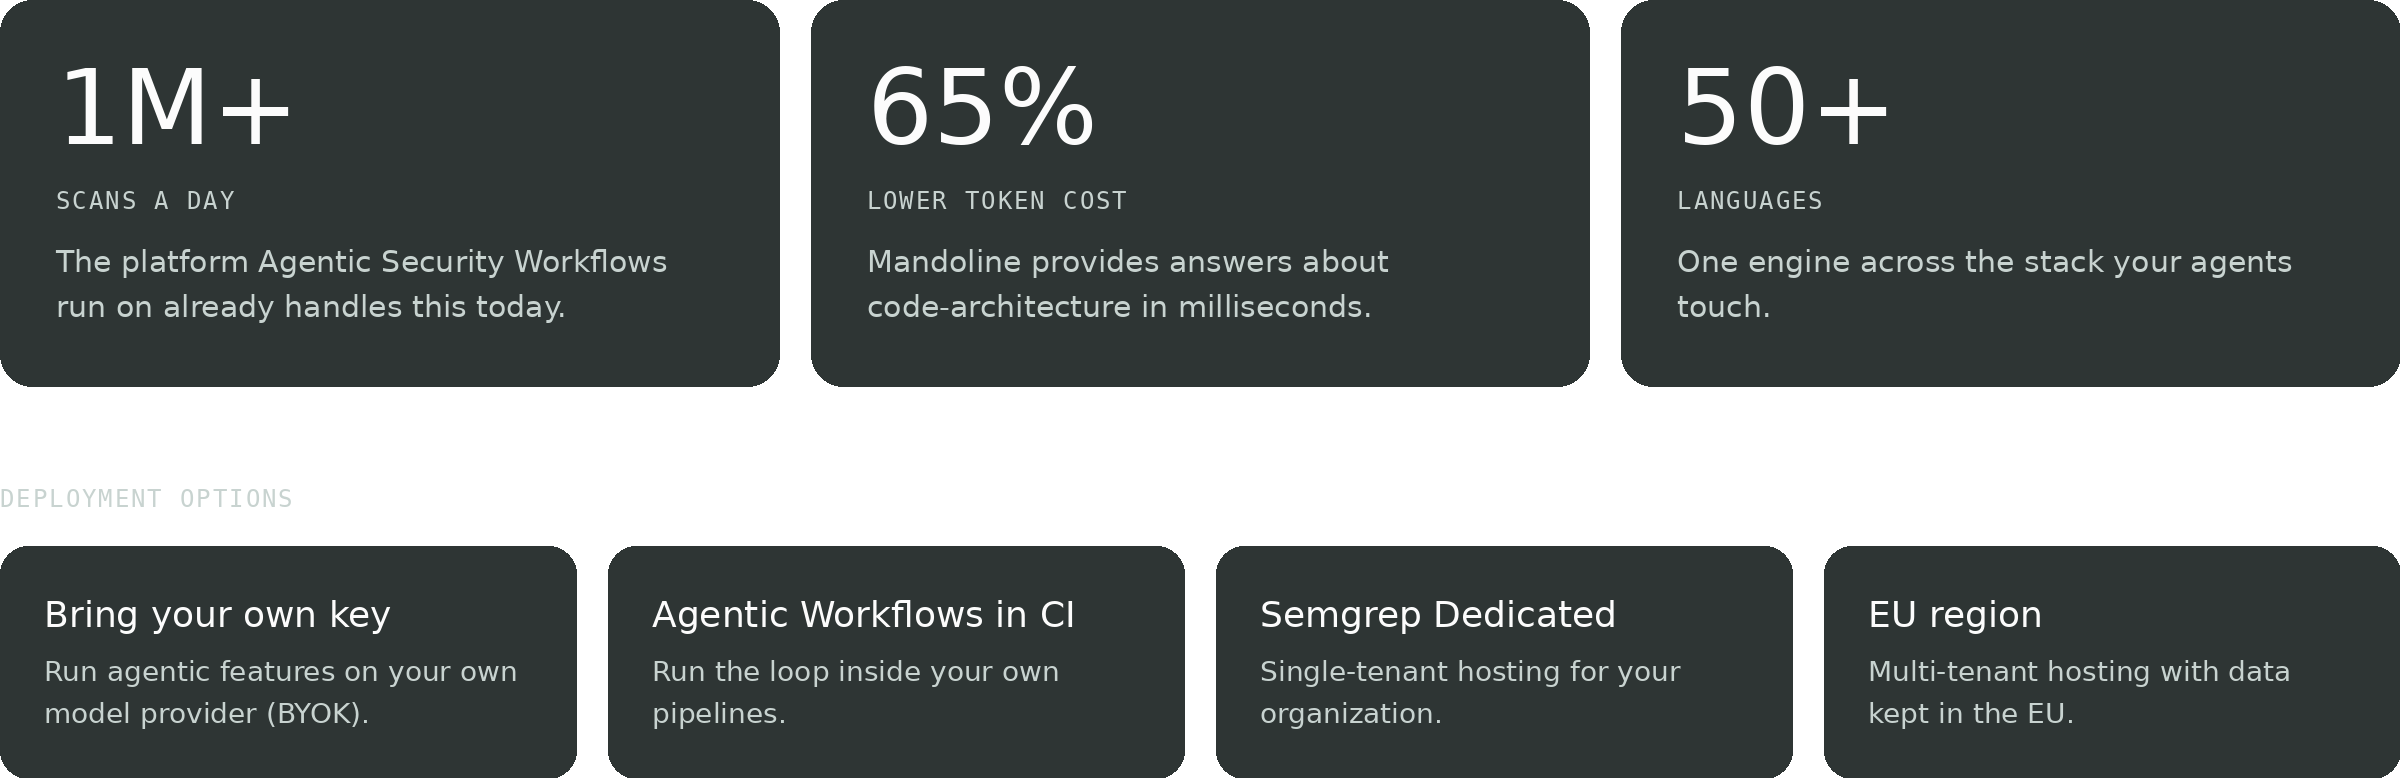
Built for scale. Deployed your way.
You wouldn't skydive without a harness.
Don't let your agents code without Semgrep.