


Code Security
for Builders and Agents
Build at the pace your agents write code. Semgrep gives every agent in your workflow the tools and context to secure code at agentic speed.

Scan and fix AI-generated code the moment it's written

Empower agents with tools and context required to automate threat detection, triage, and remediation.

Find and fix the issues that matter in your code (SAST)

Fix vulnerabilities in open source dependencies and block malware

Find and fix hardcoded secrets with semantic analysis

Protect against software supply chain attacks

Automate and Scale AppSec with Agentic Code Security

Give any agent access to the full Semgrep suite

Protect Your Code with Secure Guardrails

Ship faster, without compromising on security.

Increase security while accelerating development

Want to read all the docs? Start here

Get the latest news about Semgrep
See how Semgrep can save you time and money

Join the friendly Slack group to ask questions or share feedback
Join us at a Semgrep Event!
See why users love Semgrep
View our library of on-demand webinars
Code Security
for Builders and Agents
Build at the pace your agents write code. Semgrep gives every agent in your workflow the tools and context to secure code at agentic speed.


Built for Builders, Trusted by Security
Lives where developers work, delivering fixes without breaking flow. Gives security teams visibility, control, and confidence.


Industry-leading SAST, SCA, and secrets scanning in one high signal AppSec platform.

Secure code as it’s written. Built-in guardrails guide safe fixes before code ships.

AppSec teams triage 80% fewer false positives across SAST and SCA. Backlogs shrink, and engineering velocity climbs.

AI learns your code context to eliminate false positives and prioritize reachable vulnerabilities – validated by 95% of security reviewers across 6M+ findings.
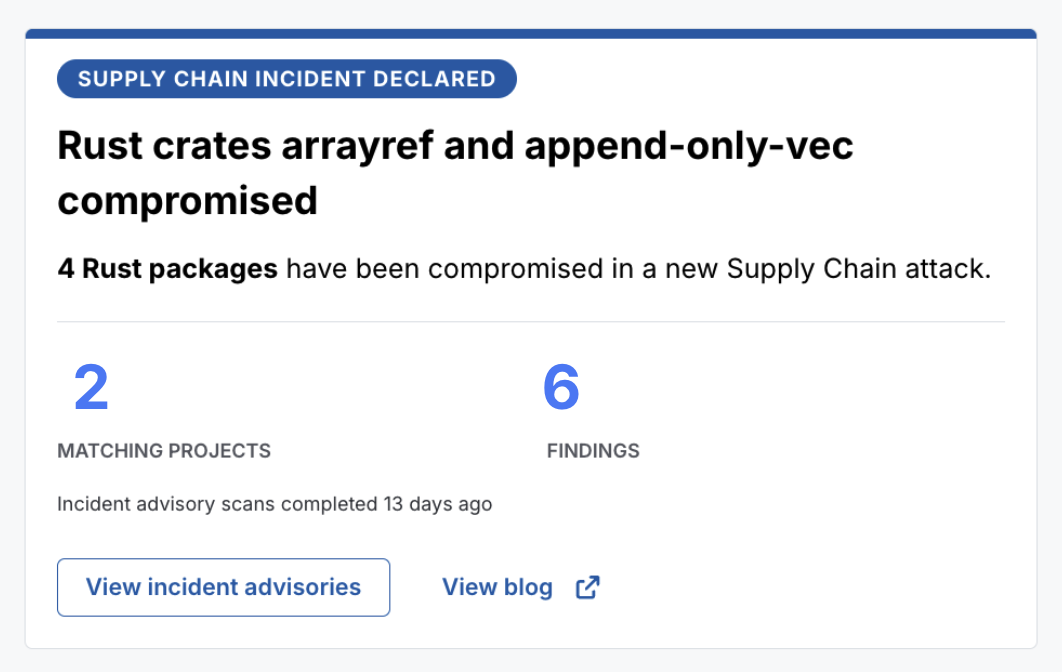
24/7 on-call security monitoring triggers an incident scan within 30 minutes of discovery. Teams get notified by Semgrep and can see the latest malware findings on their dashboard or via API.
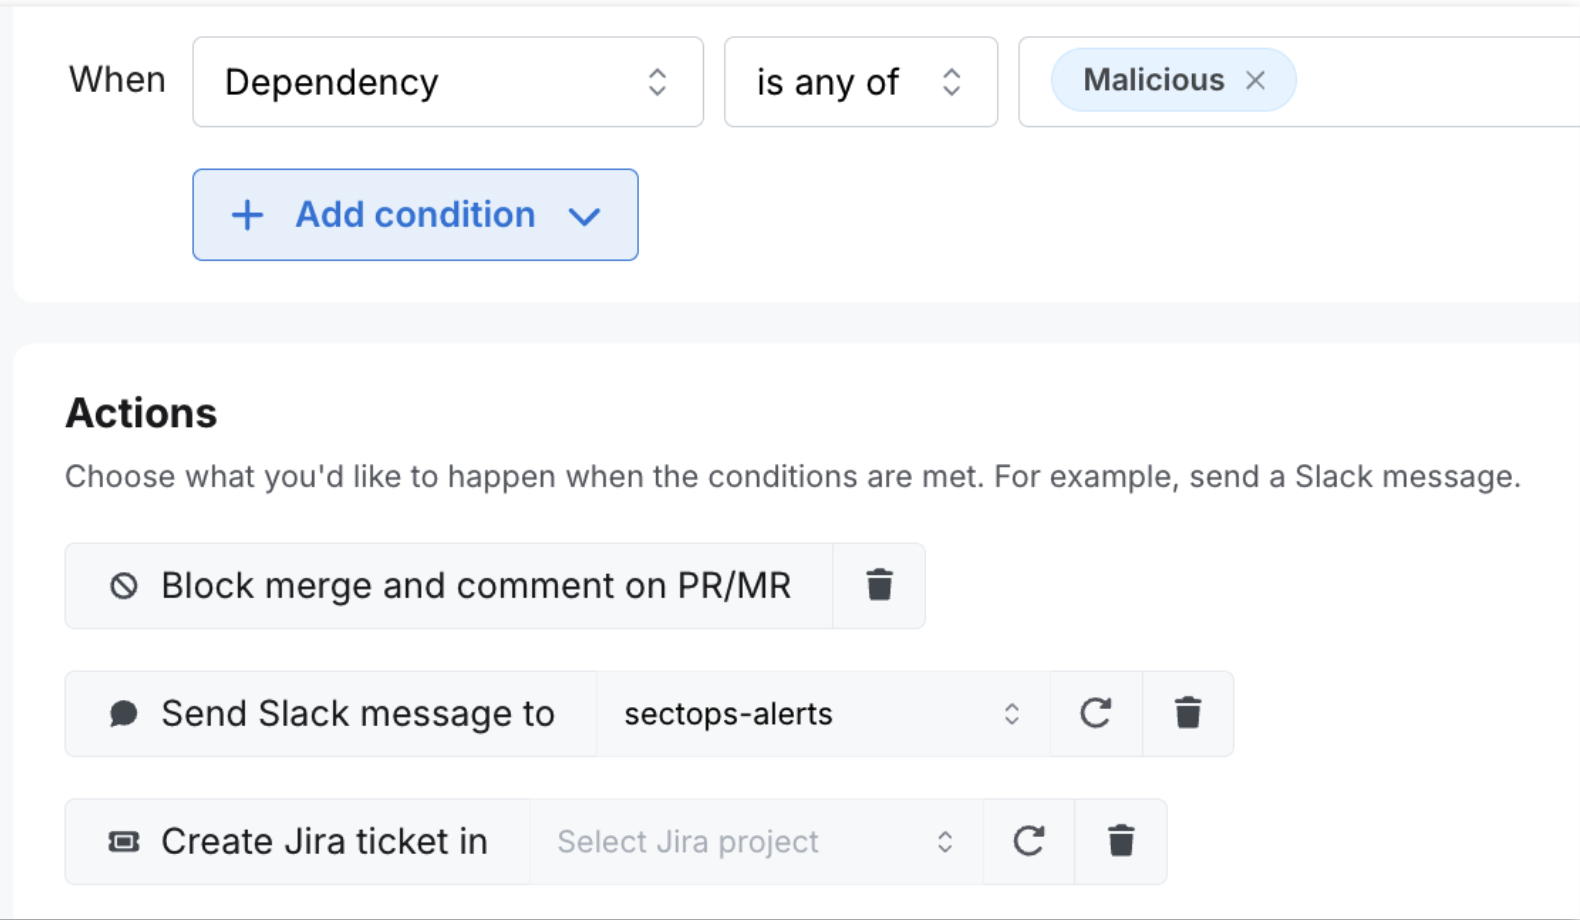
Enterprise-grade policies, with Slack and JIRA integration, take malware findings and trigger predefined remediation workflows, for end-to-end incident response automation.
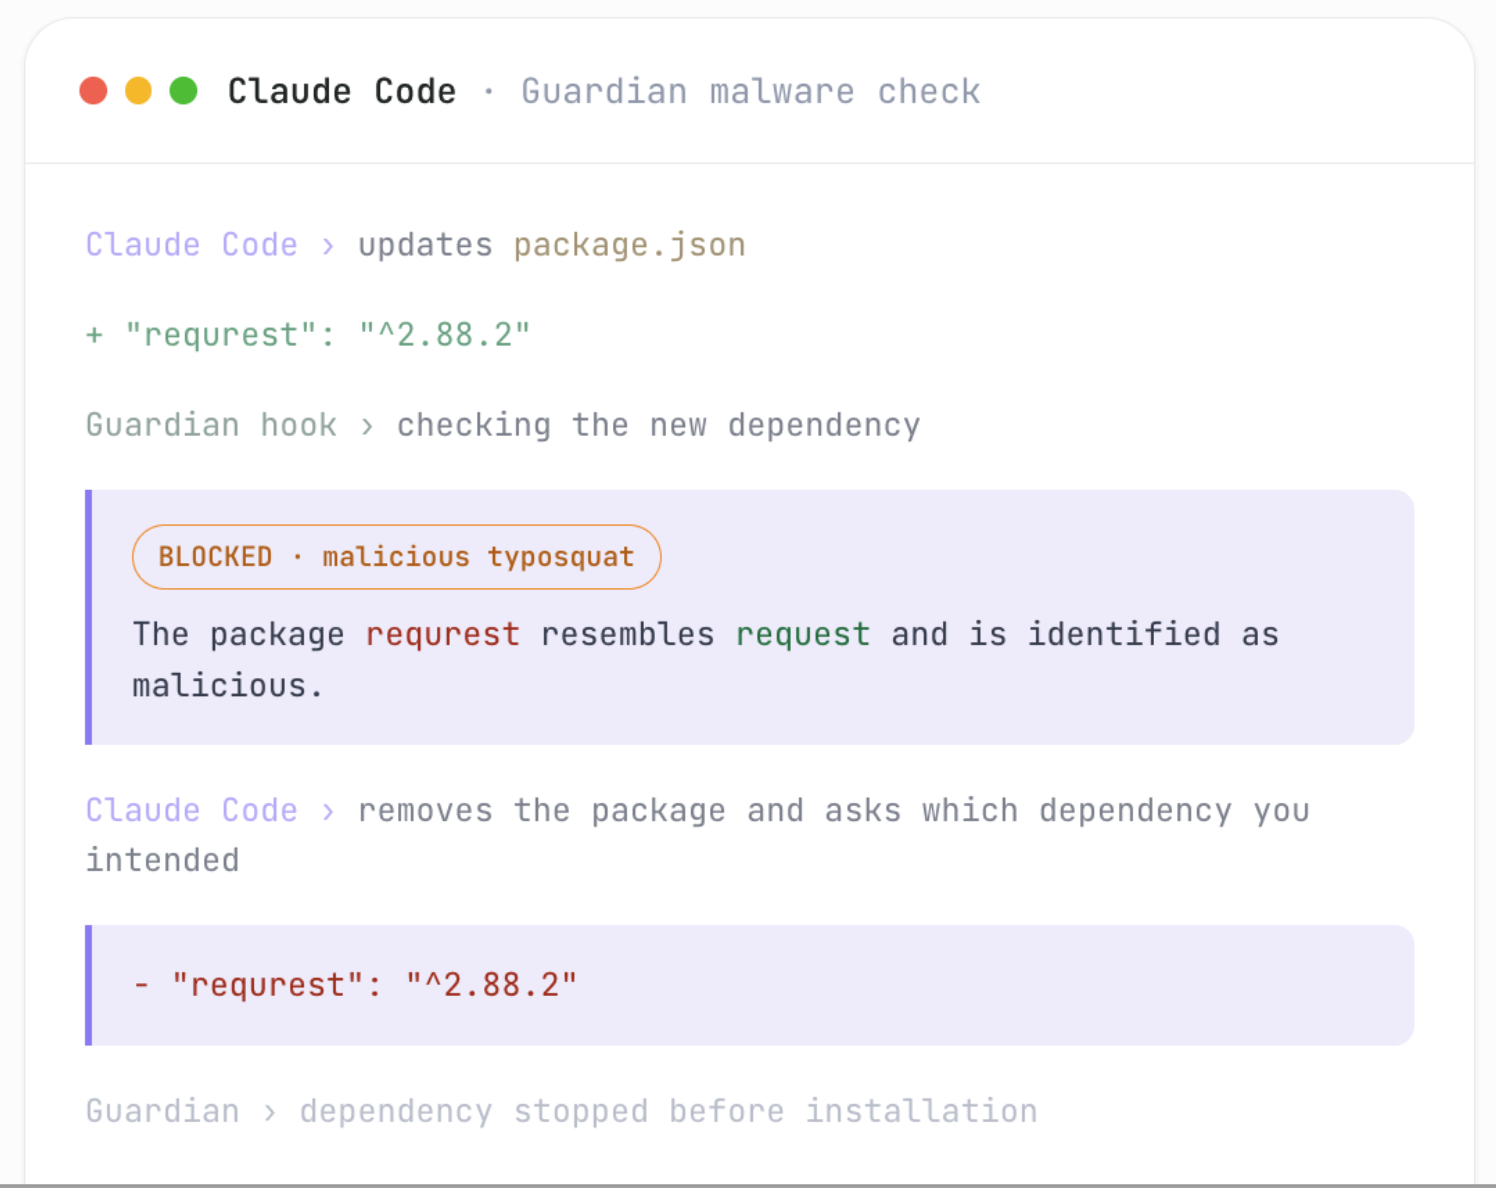
Semgrep Malware Firewall runs silently on developer machines, intercepting network requests to any public registry and blocking malicious and compromised open-source packages from reaching your environment.
Detect What Matters
Detect complex issues like IDORs, broken authorization, and multi-step logic flaws.
Combine deterministic static analysis with AI reasoning to understand naming, structure, and developer intent – going beyond pattern matching.

Noise Filtering
Prioritize what matters. Eliminate what doesn’t. Automatically triage findings using code context, patterns, and prior decisions.
Provisionally ignore false positives so AppSec teams focus on real risk. Don’t audit alerts. Automate them away.

Remediation
Turn findings into safe, actionable fixes – fast. Generate tailored remediation and upgrade guidance directly in PRs and IDEs.
Security stops being a blocker. Developers fix issues safely with confidence, not guesswork.

Prevention
Learn once, prevent forever. Human triage decisions create reusable “memories” that suppress repeat false positives automatically. Signal compounds over time. False positives don’t come back.

Works where you build. Connects where your software runs
Supported workflows and integrations:

No buzzwords, just
real world results


"Semgrep helped surface valuable context and recommendations to developers, aiding in the quick identification of false positives and remediation of legitimate findings. There were times where it just felt magical."
“We use Semgrep to provide remediation guidance to our developers directly in PR comments. Semgrep gives them additional context that helps them fix vulnerabilities quicker.”
"The ability to have Semgrep remember what I told it and automatically triage for me in the future is game changing. I have to spend a lot of time verifying the validity of vulnerabilities and being able to essentially hit the "save" button on the work I've done and just pass it on to Semgrep has really helped streamline my triage process."
Code security for builders and agents
