Semgrep Secrets
Go beyond regex: leverage Semantic Analysis, entropy analysis, and validation to accurately detect and fix secrets.

Find and fix the issues that matter in your code (SAST)

Fix vulnerabilities in open source dependencies and block malware

Find and fix hardcoded secrets with semantic analysis

Scan and fix AI-generated code the moment it's written

Combine AI reasoning with rule-based analysis for detection, triage, and remediation

Automate, manage, and enforce security across your organization

Build and deploy security pipelines that combine static analysis with AI at scale

Protect against software supply chain attacks

Increase security while accelerating development

Prevent the most critical web application security risks

Protect Your Code with Secure Guardrails

Mitigate software supply chain risks
Increase security while accelerating development

Want to read all the docs? Start here

Get the latest news about Semgrep
See how Semgrep can save you time and money

Join the friendly Slack group to ask questions or share feedback
Join us at a Semgrep Event!
See why users love Semgrep
View our library of on-demand webinars
Semgrep Secrets
Go beyond regex: leverage Semantic Analysis, entropy analysis, and validation to accurately detect and fix secrets.
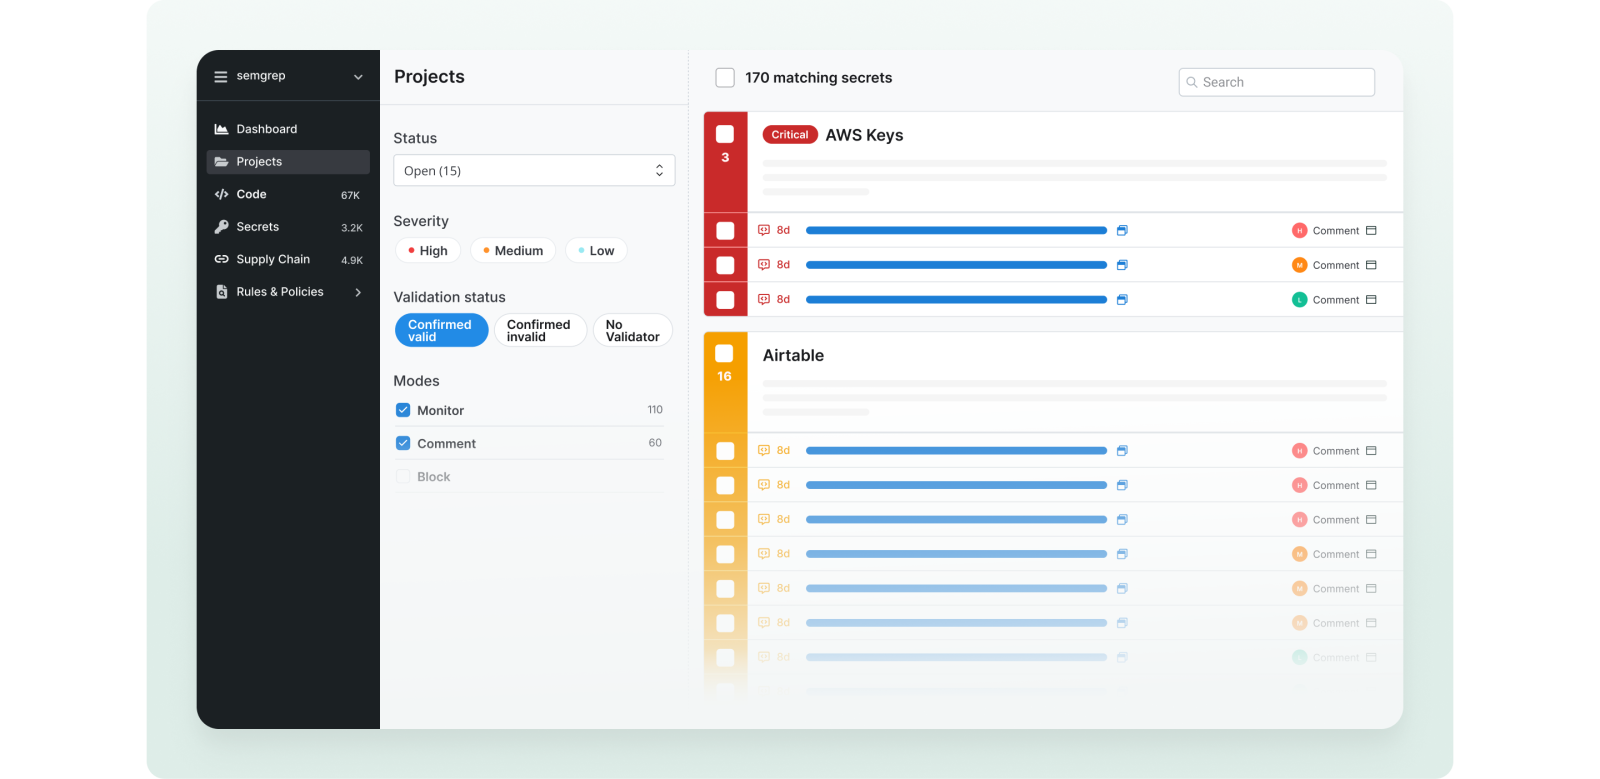


Detect secrets with high precision
Prevent secrets leaks early in development
How it works
Semgrep Secrets uses OSS + Pro Engines to find secrets specific to your code.

Semgrep Secrets can scan thousands of lines of code and look for hardcoded secrets, API keys, and other sensitive data in a few minutes using Semantic Analysis, entropy analysis, and regex.

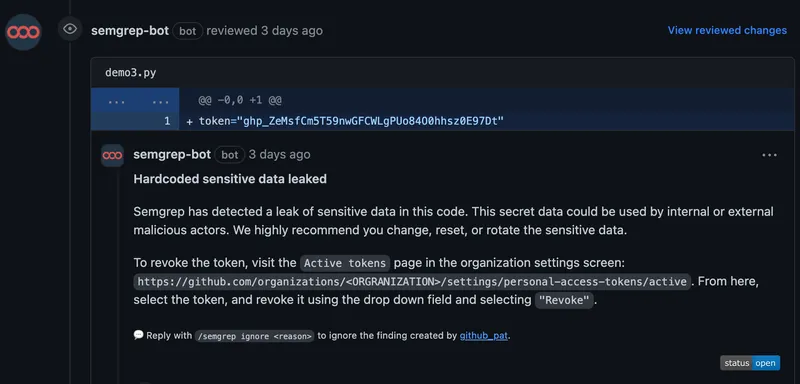
Semgrep sends a request to the corresponding service (e.g., AWS, Slack, or GitHub) to determine if the token is still valid. This happens locally within your infrastructure; we don’t send the secret to Semgrep’s servers.

Validated secrets are surfaced to developers in their workflow as PR comments so that developers can fix them as soon as possible.
Single pane of glass for security issues
Protect your code with secure guardrails

Figmates get actionable security feedback in their PRs, while rule analytics give the security team feedback on the effectiveness of our rules. The simple syntax lets us extend Semgrep to catch new patterns, going from idea to live in an hour.